Audit: Auditing and compliance reporting
Report cards, over 500 predefined reports and field-level change tracking, so your security posture and your audit evidence come from the system rather than from a spreadsheet somebody maintains.
For companies using IBM i who need to ensure their servers are protected from growing cybersecurity threats and reduce the burden of achieving regulatory compliance, Fresche Security Suite delivers strong security management to protect business-critical data and operations while helping simplify and automate compliance.
IBM i runs mission-critical daily operations for many Fortune 500 and Global 2000 companies, and it holds the data those operations depend on. The suite gives you the controls to defend that system and the reporting to demonstrate compliance, without asking your team to become IBM i security researchers first.
Six modules that share one console, one rules model and one reporting engine. Licensed together or individually, depending on where your gaps are.
Compliance report cards, over 500 built-in reports, data-level change tracking and job activity monitoring.
Network and socket access control, object and IFS security, command security and privileged access management.
Real-time monitoring of IBM i security events with flexible alerting and forwarding to any SIEM.
Field-level encryption, masking and scrambling of sensitive and personally identifiable data.
An additional authentication factor at sign-on for end users, delivered as a module of Secure.
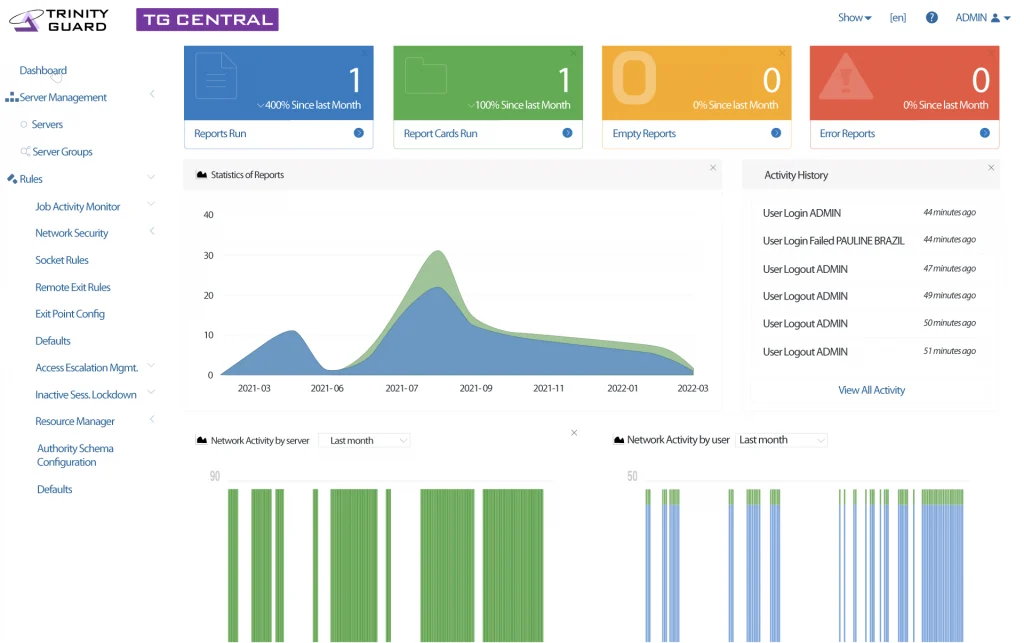
One web console to manage and audit security across every IBM i system and LPAR you run.
A secure cloud environment does not make your IBM i is secure. Our experts answer questions submitted by IBM i professionals on where that assumption breaks down.
Watch NowEvery module solves one problem completely. Most customers start with the gap that is causing pain now, then add the next once it is in production.
Report cards, over 500 predefined reports and field-level change tracking, so your security posture and your audit evidence come from the system rather than from a spreadsheet somebody maintains.
More than an exit point solution. Secure governs who reaches your data, through which door, with which authority, and keeps the record that justifies it.
There are numerous sources of security event data on IBM i and never enough time to review everything. Detect watches the sources that matter and tells you when something is not routine.
Protect specific fields inside database files, so sensitive and personally identifiable information stays unreadable to anyone without a reason to see it.
An additional layer of authentication for end users signing on to IBM i, delivered as a module of Secure and managed alongside the access rules already there.
Many servers, multiple OS levels and numerous users can create a security management nightmare. Central turns that into one dashboard and one place to configure it all.
IBM i security tooling has a long history, and much of what is installed today was assembled one product at a time.
We will walk your requirements against the suite, run a security assessment on your system and give you a free IBM i security implementation plan showing where the gaps are and what closing them involves.